Someone leaves. What did they see?
A signed receipt per person or agent: everything Gitfence served them, and when. Anyone you send it to can check it.
"What did the contractor we just let go see?"
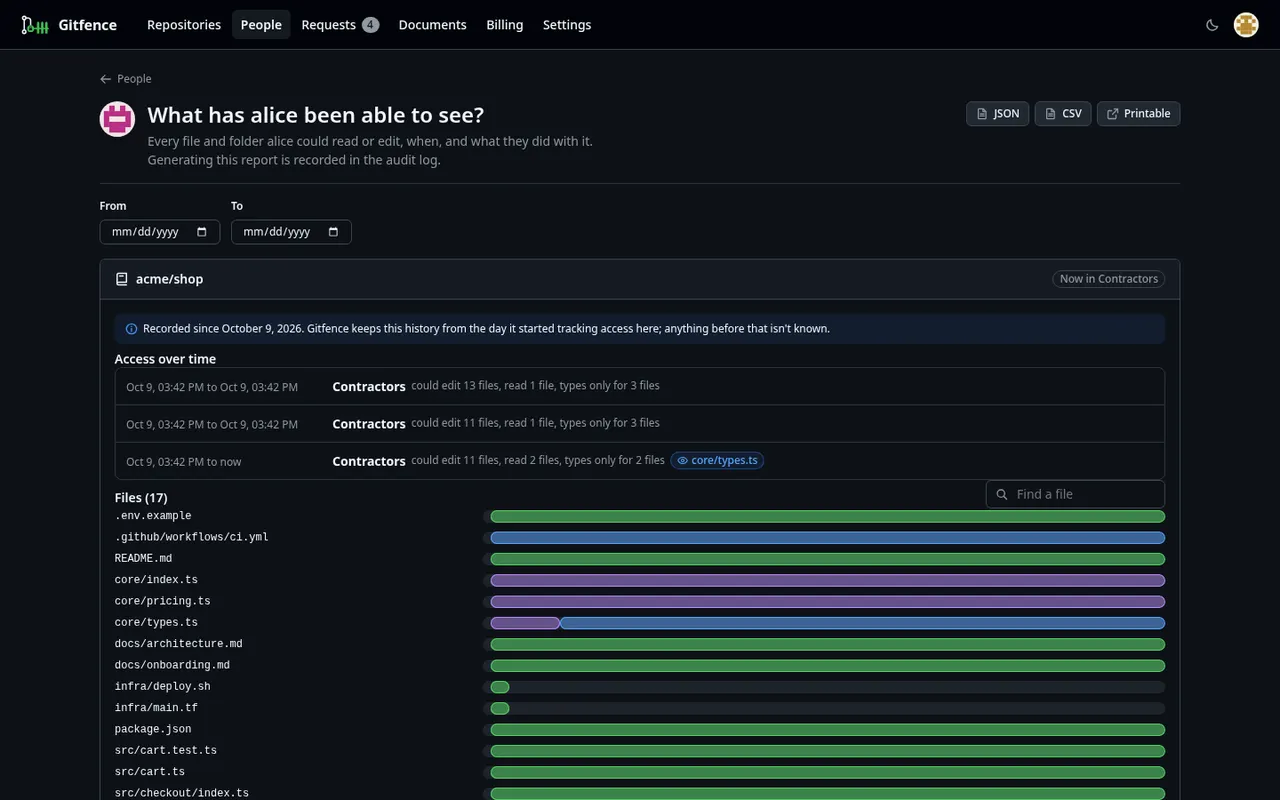
Every file they could read or edit, with dates. Every clone, fetch and push. Every document they signed. Export it for the file.
"What could our AI agents have sent to an AI provider?"
At most, what Gitfence served to them. The receipt lists it per agent, and the repository attestation lists the files never served to any AI agent.
What's in a report
What was served
Every folder and file: as source, as types only, or never.
Per person and per agent
One receipt for alice, another for her Claude Code.
Access over time
Which folders, at which level, from when to when.
Signed
With your organization's own key, as JSON and PDF.
Anyone can verify
A public page. No account needed.
Share or withdraw
Send a link. Take it back when you want.
An upper bound, not a prompt log
It tells you the most that could have left. It can't tell you what did.
What it shows
- What each clone and fetch delivered to each person and agent.
- Which files were never served to any AI agent.
- Who could read a given file, including people who left.
What it doesn't
- Prompts, or what an agent sent to its AI provider.
- Which files someone opened after cloning.
- Clones from before Gitfence recorded them, or made straight from GitHub.
- Review comments, issues and test output, which are redacted but not listed.
A receipt your client can check
Send it. They verify it without an account, and without taking your word for it.
For your client
One page per repository: who was served what, and what no AI agent ever got.
Signed, not just exported
Change one character and it stops verifying.
Leak tracing
A marker in each copy can tie leaked text to one person. Not every leak carries it.
Questions
Is this a log of what our agents sent to an AI provider?
No. Gitfence never sees prompts. The report shows what Gitfence served to that agent's clone, which is the most the agent could have read or sent anywhere. Treat it as an upper bound.
How far back does a report go?
To the day you set up Gitfence. What someone could reach before that isn't known. Reports follow the default branch only.
Can I see who could read one sensitive file?
Yes. Pick a path and the report lists everyone who could read it, and when, including people who have since left.
Are the reports signed?
Yes. A receipt is signed with your organization's own Ed25519 key and comes as JSON and as a PDF that carries the same JSON. Change one character and it no longer verifies.
How does someone outside our company check a receipt?
They paste or upload it at gitfence.dev/verify. No account is needed. You can also send a share link and withdraw it later. Your public keys are published, so a receipt can be checked without asking our server.
What does "never served to any AI agent" mean?
The repository attestation lists the files that Gitfence did not serve to any agent during the period. It covers what went through Gitfence by git. It says nothing about agents run by people who clone straight from GitHub.
Can a leak be traced to one person?
Sometimes. Each person's copy carries a harmless marker in the text Gitfence generates: the agent guide, the headers of generated types and the stand-ins for secrets. Paste leaked text into Gitfence and it names the copy. Ordinary source files carry no marker, and someone who knows about it can delete it.
Know the answer before someone asks
Fence the repo today and every report starts from today.